T1#security#regulation#open-source#market
Claude Mythos Preview and Project Glasswing — The Model Held Back for Its Hacking Skill
Metadata
- Date
- Decade
- 2020s
- Tier
- T1
- Timelines
- A History of Artificial Intelligence · AI and Society: A History · A History of Cybersecurity
- Sources
- 07
- Connections
- 08
- Tags
- #security#regulation#open-source#market
On 7 April 2026 Anthropic announced Claude Mythos Preview, a general-purpose frontier model that it chose not to release to the public, and Project Glasswing, an initiative to put the model to work for defenders first. The reason, in Anthropic's account, was the model's skill at computer security: over the previous weeks, the company said, Mythos Preview had found thousands of zero-day vulnerabilities — flaws previously unknown to the software's developers — many of them critical, in every major operating system and every major web browser.
Glasswing's launch partners were Amazon Web Services, Apple, Broadcom, Cisco, CrowdStrike, Google, JPMorganChase, the Linux Foundation, Microsoft, NVIDIA and Palo Alto Networks, alongside Anthropic itself, plus more than 40 further organisations that build or maintain critical software. The decision turned a long-running debate about AI and hacking into a practical question for banks, regulators and open-source maintainers.
What Anthropic said the model could do
The details came in a post on Anthropic's Frontier Red Team blog the same day. Anthropic said that more than 99% of the vulnerabilities it had found were not yet patched, so it could describe only a small fraction; for many others it published cryptographic hashes, promising to reveal specifics after fixes.
| Example (Anthropic's account) | Detail |
|---|---|
| OpenBSD | A 27-year-old flaw, the oldest found so far, in an operating system known for its security; it let an attacker remotely crash a machine just by connecting to it |
| FFmpeg | A 16-year-old flaw in the H.264 decoder, in a line of code that automated testing had hit five million times without catching the problem |
| Linux kernel | Several vulnerabilities found and chained autonomously to escalate from ordinary user to full control of the machine |
| FreeBSD | A remote-code-execution exploit against the NFS server giving unauthenticated users root, built from a 20-gadget ROP chain split across several packets |
| Firefox | On bugs its previous model had found in Firefox 147's JavaScript engine, Mythos Preview produced working exploits 181 times; Claude Opus 4.6 had managed it twice in several hundred attempts |
Anthropic gave cost figures for the OpenBSD search: a thousand runs of its scaffold cost under US$20,000 and turned up several dozen further findings; the run that found the headline bug cost under US$50, though Anthropic stressed that this number only makes sense with hindsight. To check its severity ratings, it had expert contractors review 198 reports manually: they agreed with the model's rating exactly in 89% of cases and within one level in 98%.
The company said it had not trained the model specifically for these skills; they emerged from general gains in coding, reasoning and autonomy. It also wrote that engineers with no formal security training had asked the model to find remote-code-execution bugs overnight and woken to a complete, working exploit — the clearest statement of why it thought general release was unsafe.
What Glasswing was
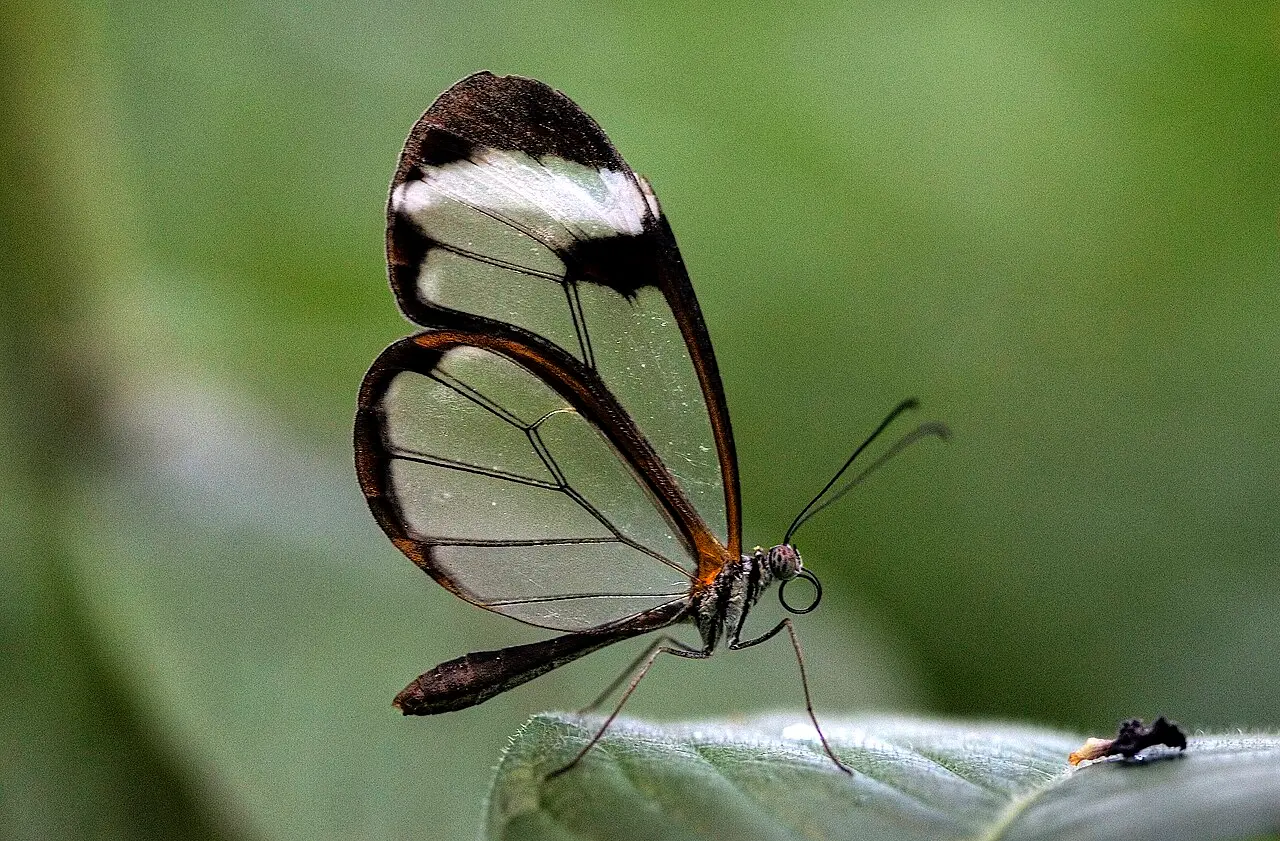
Glasswing was a controlled-access programme with money attached. Anthropic committed up to US$100 million in usage credits for Mythos Preview and US$4 million in donations — US$2.5 million to Alpha-Omega and OpenSSF through the Linux Foundation and US$1.5 million to the Apache Software Foundation. After the credits, participants would pay US$25/US$125 per million input/output tokens, through the Claude API, Amazon Bedrock, Google Cloud's Vertex AI or Microsoft Foundry. The name comes from the glasswing butterfly, Greta oto, whose transparent wings let it hide in plain sight — like the vulnerabilities, Anthropic wrote.
Anthropic said it did not plan to make Mythos Preview generally available and would first test new safeguards on an upcoming Claude Opus model. It promised a public report within 90 days, and wrote that an independent third-party body might in the medium term be the ideal home for such work.
Reaction
Government and finance. Within days, multiple outlets reported that Treasury Secretary Scott Bessent had convened the chief executives of Bank of America, Citigroup, Wells Fargo, Goldman Sachs and Morgan Stanley in Washington, with Federal Reserve Chair Jerome Powell also reported to be involved, to discuss the cyber risks. A Treasury spokesman said the meeting was meant to begin forming an approach to the rapid developments in AI.
Partners. The launch quotes were emphatic. Cisco's Anthony Grieco said AI capabilities had "crossed a threshold"; CrowdStrike's Elia Zaitsev said the window between discovery and exploitation had collapsed. The Linux Foundation's Jim Zemlin framed it as a chance to give open-source maintainers security expertise they had never been able to afford.
Skeptics. On 18 April The Decoder reported tests by the AI security firm AISLE: given the code snippets Anthropic had published, all eight models it tried — including a small open model — caught the FreeBSD memory bug, though none reproduced Mythos's exact exploit technique, and results on the OpenBSD bug varied widely. The researchers' conclusion was that the surrounding system matters as much as the model. On 11 May curl's Daniel Stenberg reported that of five "confirmed security vulnerabilities" Mythos had flagged in curl, one was real, and low severity; he concluded that "the big hype around this model so far was primarily marketing", while still rating AI code analysers far above traditional ones. The Decoder also cited Financial Times reporting that Anthropic was holding the model back partly until it had enough compute to serve customers.
The bottleneck moves
Anthropic's first update, on 22 May, reframed the problem. With roughly 50 partners, it said, Mythos Preview had found more than ten thousand high- or critical-severity vulnerabilities in a month. Progress used to be limited by how fast bugs could be found; now, Anthropic wrote, it was limited by how fast they could be verified, disclosed and patched.
| Figure (Anthropic, 22 May 2026) | Value |
|---|---|
| Cloudflare: bugs found in critical-path systems | 2,000 (400 high or critical) |
| Mozilla: vulnerabilities fixed in Firefox 150 | 271 |
| Open-source projects scanned | more than 1,000 |
| High/critical findings independently assessed | 1,752, of which 90.6% valid |
| High/critical bugs disclosed to maintainers | 530, of which 75 patched |
It reported that the UK AI Security Institute had found Mythos Preview the first model to solve both its cyber ranges end to end, and that some maintainers — already swamped by low-quality AI reports — had asked Anthropic to slow its disclosures. Microsoft said its patch volumes would "continue trending larger for some time". The burden that XBOW and curl had exposed in 2025 had arrived at industrial scale.
What followed
In June the successor model, Mythos 5, went to Glasswing partners and was briefly caught up in a US export-control order; that episode is covered in AI model export controls (2026). The same month's Executive Order 14409 built a federal framework for "covered frontier models" around exactly this kind of cyber capability.
On 6 October 2026 Anthropic folded Glasswing into an expanded Cyber Verification Program with three access tiers, moving existing Glasswing members to its most permissive tier. It said partners had uncovered at least 129,000 verified vulnerabilities between April and July 2026, plus 5,500 from its own open-source scanning, based on survey data from a subset of partners. Those numbers are Anthropic's, as are almost all the figures in this story. The shift they describe, in Anthropic's framing, is that by late 2026 finding software flaws had become cheap, and the scarce resource was the human time to fix them.
Background: Claude, the earlier GTG-1002 espionage report, Google's Big Sleep, and the cybersecurity and AI timelines.
Questions this page answers
- What is Claude Mythos Preview?
- It is a general-purpose frontier model Anthropic announced on 7 April 2026. Citing its security capabilities, the company declined to release it publicly and offered it only to organisations securing critical software through Project Glasswing.
- What is Project Glasswing?
- It is Anthropic's restricted-access programme for using Mythos Preview defensively. Launch partners were AWS, Apple, Broadcom, Cisco, CrowdStrike, Google, JPMorganChase, the Linux Foundation, Microsoft, NVIDIA and Palo Alto Networks, plus more than 40 other organisations. Anthropic committed up to US$100 million in usage credits and US$4 million in donations. It is named after the glasswing butterfly.
- Did Mythos Preview really find thousands of zero-days?
- That is Anthropic's claim. Because over 99% were unpatched, details were withheld and the total could not be checked from outside. AISLE showed smaller models could find some of the published examples, and curl's Daniel Stenberg reported that only one of five 'confirmed' curl findings was real, and low severity. On the other hand, Anthropic reported that Mozilla fixed 271 vulnerabilities in Firefox 150.
- What happened to Mythos afterwards?
- In June 2026 the successor Mythos 5 went to Glasswing partners and was briefly suspended under a US export-control order. On 6 October Anthropic folded Glasswing into an expanded Cyber Verification Program, moving its members to the least restricted tier.
Sources
PrimaryProject Glasswing: Securing critical software for the AI era — Anthropic, Apr 7, 2026
Launch partners, 40+ further organisations, the 'thousands of zero-days' claim, the OpenBSD, FFmpeg and Linux examples, US$100M and US$4M, pricing, the no-general-release policy, the origin of the name
Over 99% unpatched, the FreeBSD NFS exploit, 181 versus two Firefox exploits, the OpenBSD search cost, 89% and 98% agreement on 198 reviewed reports
PrimaryProject Glasswing: An initial update — Anthropic, May 22, 2026
Over ten thousand findings with about 50 partners; Cloudflare; Mozilla's 271; the UK AISI; open-source scanning results; maintainers asking to slow disclosures
AISLE's tests; the Financial Times report it cites
Last updated: